
YubiKey setup
Do this once when you receive a new YubiKey. After that, configure each PC separately: YubiKey PC setup.
Verify that you have a genuine YubiKey.
PIV
Prerequisites:
- Install YubiKey Manager CLI
- Have your PIN and Management Key ready (store in Vaultwarden)
- Use a supported algorithm (see Supported algorithms below)
You must set your pin-policy at key creation. You cannot change it afterwards (you must create new keys). Use once (not always) if you need agent forwarding.
- Generate a keypair (select one of the working algos: prefer
eccp384overrsa3072overrsa2048):
ykman piv keys generate --touch-policy never --pin-policy once -a eccp384 9a pubkey.pem- Create a self signed cert based on this key:
ykman piv certificates generate 9a pubkey.pem --subject "CN=SSH Key" --valid-days 36500- On a PC with OpenSC installed (see YubiKey PC setup), retrieve your public key and add it to
~/.ssh/authorized_keyson the remote host:
ssh-keygen -D "C:\Program Files\OpenSC Project\OpenSC\pkcs11\opensc-pkcs11.dll"Supported algorithms
Known working algos are:
- rsa1024 (probably, pls don't use)
- rsa2048 (default)
- rsa3072
- eccp384 (sign-only, no de/encryption, prefer this for ssh)
Unsupported (or known to fail):
- rsa4096
- ed25519
- x25519 (failed on certificate creation)
GPG
Create OpenPGP Key
You can create a GPG-Key (e.g. for Sysreptor Archiving) as described here: Archiving | SysReptor (Tab: "Generate private keys on YubiKey 5").
List your Public-Key with
ssh-add -LIf the command returns "The agent has no identities.", make sure you complete the YubiKey-PC-Setup first.
For every Key you want to use as a SSH-Key add its Keygrip to C:\Users<user>\AppData\Roaming\gnupg\sshcontrol.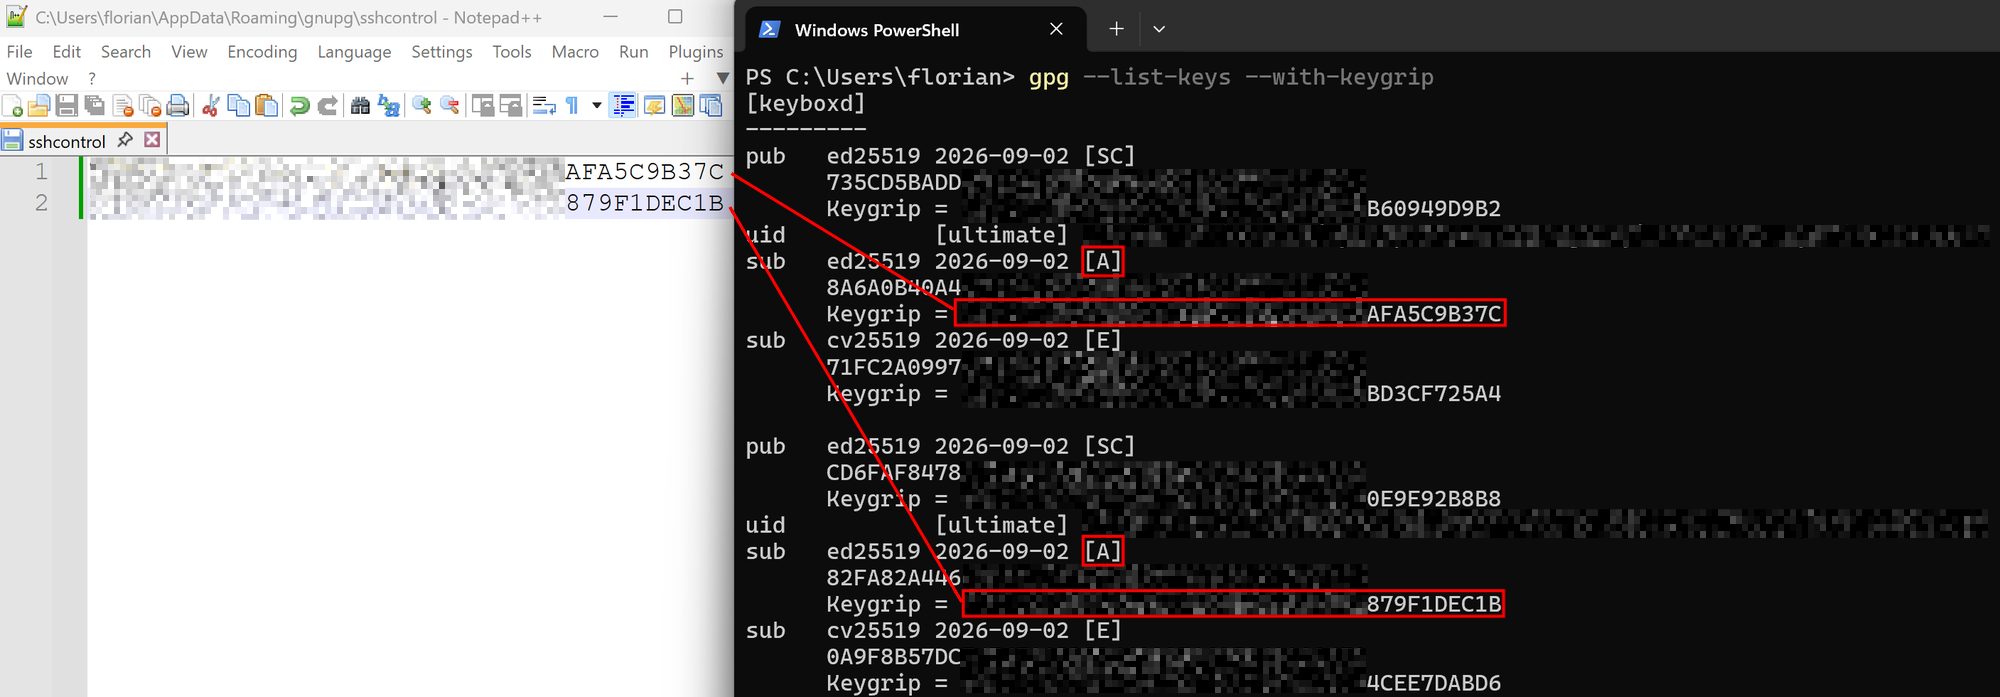 .